Types of Information Warfare: What the Categories Leave Out
The standard taxonomy of information warfare tells you what kinds of attacks exist. It does not tell you which ones are aimed at you, and that gap is where executive risk lives.
Understanding the types of information warfare is the starting point for defense, and the categories themselves are not a map of your exposure. A taxonomy tells you what kinds of attacks exist somewhere in the world. It does not tell you which of them has your name, your filings, and your family's addresses already attached. That distinction decides whether you spend your budget on defense or on a reading list.
The academic literature has been sorting these operations for decades. A 2007 chapter in the Encyclopedia of Digital Government sorted them into distinct types. Both are useful. Neither answers the question a sitting executive actually has on a Monday morning, which is: which one is pointed at me, and what do I do first?
What the Taxonomy of Information Warfare Actually Describes
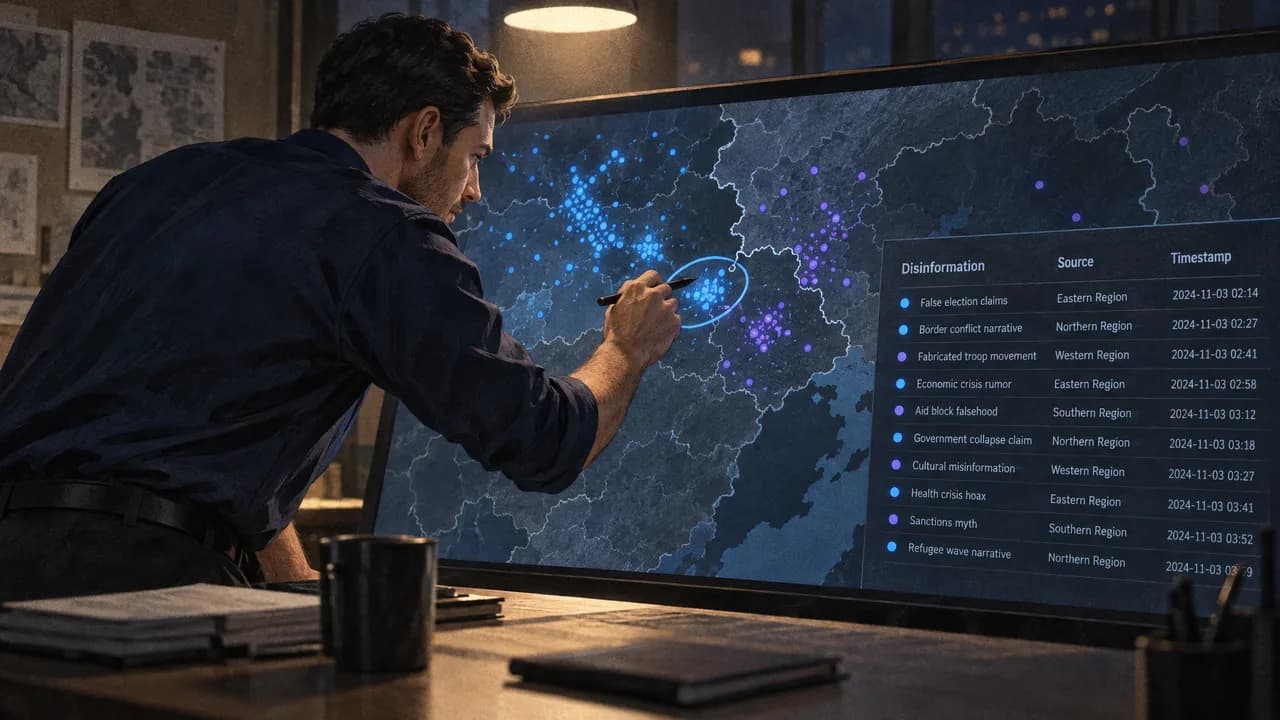
Information warfare takes place within the information environment, the aggregate of individuals, organizations, and systems that collect, process, disseminate, or act on information, as the University of Washington's Jackson School of International Studies frames it. Read that definition slowly, because it contains the whole problem. The environment has three parts: the people, the institutions, and the systems. Most defense spending covers the third one and ignores the first two entirely.
That framing has held since at least the 2000 EDPACS treatment of information warfare and security. What changed is not the definition. It is who qualifies as a target. When the concept belonged to militaries, the environment was someone else's country. Now it is a search index, a corporate registry, a conference attendee list, and a data broker's inventory, all keyed to your legal name.
There is a version of this idea that executives keep running into, where the definition gets framed as a nation-state problem and quietly stops being about them. We would point you to our own working definition of information warfare that executives actually need if that framing has already cost you time.
What the Term Covers in Practice
Information warfare is the deliberate use of information, or the denial of it, to change what a target believes, decides, or can do. The word "deliberate" carries the weight. NATO defines disinformation as false or inaccurate information spread deliberately to manipulate the opinions and actions of others, and that deliberateness is what separates the category from ordinary noise, bad journalism, and a competitor's optimistic press release.
Four broad families come up in practice. False or manipulated content is the one people picture. Exposure operations, where accurate personal data gets published or threatened with publication, do more damage to executives and rarely make the news. Collection, the quiet assembly of a target's data from public and commercial sources, feeds the other two. Availability operations, from takedowns to network intrusions, close the set.
The overlap matters more than the boundaries. An operator who has spent three weeks collecting your address history, your board memberships, and your spouse's employer is already positioned for whichever of the other three families pays. Categorizing the attack after it lands is a post-mortem exercise. Mapping your exposure before it does is defense.
How an Attack Against a Named Person Comes Together
By 2022, information warfare had become mainstream enough that aspects of it were being reported in the national press, as the Australian Army's Cove publication noted that year. Mainstream coverage produced a predictable side effect: the topic now reads as geopolitics rather than personal risk. The mechanics say otherwise. The same collection techniques work on a company's leadership team, at a fraction of the effort, with a much shorter path to a payout.
This is the part that does not appear in the categories, and it is worth walking through our executive-facing explanation of how these operations unfold if you want the full chain. The short version follows.
The collection layer is the foundation
An operator starts with free material: property records, court filings, corporate registrations, professional bios, conference rosters, and the small consistencies people leave across platforms. County assessor databases and state business registries are public by design. Nothing criminal happens in this phase, which is exactly why it goes unnoticed.
The aggregation layer adds purchased data
Data brokers fill the gaps. Marketing records hold email addresses and phone numbers, loyalty programs hold purchase patterns, and people-search sites resell the combination in a single query. A public record gives an attacker an address. A broker record gives them the address, the previous three, the phone number, and the relatives who might answer.
The dissemination layer is where damage lands
Exposing a home address, seeding a false claim about a CEO's conduct, or spoofing a board member's voice to a controller are different attacks built from the same cached material. Take away the material and all three get harder. This is what makes the collection layer the correct place to fight, even though it produces none of the drama that gets a security budget approved.
The Order of Operations That Holds
Sequence matters because exposure is layered, and the layers have different removal paths. Working out of order wastes money on the outer edges while the foundation stays put.
- Map what is already visible, using the exact identifiers tied to you: legal name, prior names, addresses going back a decade, email addresses, and phone numbers.
- Separate what is reachable from what is not. A county property record and a broker profile both expose you, but only one is removable on request, and treating them the same wastes the effort.
- File the removals at the collection layer first, where broker records and people-search listings supply the aggregators downstream.
- Confirm that each removal actually took effect, rather than trusting the acknowledgment.
- Re-scan on a schedule, because broker inventories refill from public sources and a removal is a moment, not a state.
Step five is where most self-directed efforts die. A removal notice is a request honored on a day. The underlying public records do not change, so the record can be rebuilt from them the next time a broker refreshes. That is the loop you are managing, not a single cleanup task.
Where Experienced Operators Still Slip
The most expensive errors come from applying a threat model built for a different world. They are not beginner mistakes. They are mistakes that come from knowing the field well and trusting the wrong part of it.
Treating the taxonomy as an inventory. A leader reads the standard categories, checks that none of them looks national-security-shaped, and moves on. The taxonomy was never a threat assessment. It describes attack types in the abstract; it says nothing about which of them your job title, public filings, and media footprint have made cheap to attempt.
Assuming a private individual is not a target. This one usually arrives after someone has already been targeted. Executives running high-visibility negotiations, family offices, founders exiting a company, and litigants all carry the profile, and none of them think of themselves as public figures. The trigger is not fame. It is leverage, which is a transient condition that changes the day a deal is announced.
Waiting for the first incident because vendors feel opportunistic. The instinct is understandable, and it is backwards. Information warfare is asymmetric: preparation costs the defender time and money, and the attacker spends almost nothing to probe. There is no free trial period on this. The first observable incident is frequently the last free warning you get.
Outsourcing to a tool with no operator behind it. A subscription that generates a report nobody reads is not monitoring, it is a subscription. The signal that it is working is a person deciding something, on a schedule, about a specific found record.
When to Stop Doing This Yourself
A disciplined self-directed sweep catches real exposure. For someone with a low public footprint, no litigation, and no active deal, periodic self-checks cover the reachable ground at near-zero cost. That is a legitimate position, and we would rather say so than sell you a retainer you do not need.
The calculus changes at a specific point. Legal exposure from filings or litigation, a family office structure, a board seat at a public company, a merger or IPO in motion, or any direct threat to publish personal data: these change what an attacker can reach you with, and they change it fast. At that point periodic self-checks stop being adequate.
The gap is not scan frequency. It is that a self-check captures a moment, and a broker record disappears and reappears around it. We handle that with a different structure: an assigned guard who owns the exposure picture for one person, backed by the same collection, scanning, and testing work we run for the company. Our differentiator is not a report. It is a dedicated Digital Guard assigned per client and a continuous sweep that catches what a one-time check misses.
Here is the trade-off most operators in this space will not say out loud: an external team adds a vendor with visibility into your personal data. The offset, when the contract is written correctly, is that a written scope and retention policy governs it. A free consumer tool armed with the same access answers to nobody and sells to whoever wants it. That comparison, not coverage, is the actual decision.
Frequently Asked Questions
What are the 7 phases of unconventional warfare?
Their names vary by doctrine and by service, but the shape is consistent: shaping the environment before action, establishing a presence inside it, gathering intelligence, mobilizing partners, executing the operation, and consolidating what was taken. The phase most relevant to a targeted executive is the third. It is quiet, it produces no incident report, and by the time anyone notices, the collection that will enable the later phases is already complete.
What are the four types of cyber attacks?
The split most security teams use runs by what the attack does: unauthorized access to systems, content manipulation, disruption of service, and collection or theft of data. Treat them as endpoints rather than starting conditions. Every one of them was preceded by research, and that research usually involved public records and broker data with no security control anywhere on the path.
What are different types of warfare?
Beyond the conventional military sense, the literature divides warfare by the environment a state or group contests: land, sea, air, space, cyber, and information. The information domain is the one where a private company or an individual executive has no formal protection. There is no equivalent of a border patrol watching the search index, which is why the protection has to be arranged privately.
What are the four levels of warfare?
Doctrine typically describes strategic, operational, tactical, and sometimes the political or policy level above them. Translate that onto a personal threat landscape and it collapses into two questions that actually matter: what does the attacker want from you, and how would they reach it with the least effort. The cheapest path usually runs through public records, which is where a professional sweep starts.
Sources
Sources checked on September 24, 2026.
Get new articles by email
New articles from Area 52, sent to your inbox.
By subscribing you agree to receive emails from Area 52 about new articles. You can unsubscribe at any time.